A website can be compromised long before anyone notices a warning page or missing files. A weak administrator password, an outdated WordPress plugin, or a missed backup can give an attacker an opening that disrupts sales, damages customer trust, and consumes valuable time. This website security guide focuses on the practical controls that matter most for small businesses, online stores, agencies, and growing sites.
Website security is not one product or one setting. It is a set of layers that reduce the chance of an incident and limit the damage when something goes wrong. The right mix depends on your site, its traffic, the data it handles, and how much technical management your team can take on.
Start With the Hosting Environment
Your hosting environment is the foundation of website security. A secure website application can still be exposed by poor server configuration, unsupported software, or an account that lacks isolation from other users.
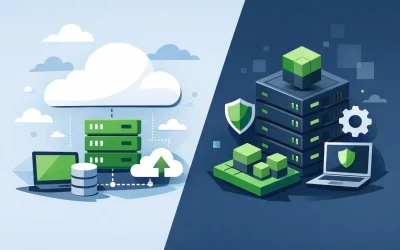
For a simple brochure site or new blog, shared hosting can be a sensible and cost-effective option when the provider maintains the server, monitors for issues, and includes basic protections such as SSL support. As a business processes more transactions, handles customer data, runs custom applications, or needs greater control, managed WordPress, cloud hosting, VPS hosting, or a dedicated server may be a better fit.
More control is not automatically more secure. A VPS gives developers flexibility, but it also places more responsibility on the account owner to patch the operating system, configure firewalls, and manage services. Managed hosting can reduce that workload by handling key maintenance tasks, although it may offer fewer configuration choices. Choose the environment that matches both your performance needs and your team’s ability to manage it safely.
Keep Server Software Supported
Unsupported PHP versions, outdated database software, and end-of-life operating systems create avoidable risk. Security patches are released because real vulnerabilities are found. Delaying updates for months can leave known weaknesses exposed to automated attacks.
Before updating a production site, confirm plugin and theme compatibility, take a backup, and test changes where possible. The goal is not to update recklessly. It is to establish a consistent maintenance schedule so updates do not become an emergency project after an incident.
Use SSL Everywhere, Not Just at Checkout
An SSL certificate encrypts traffic between a visitor’s browser and your website. It protects information such as login credentials, contact form submissions, payment details, and session data from interception. It also supports visitor confidence and helps browsers avoid displaying security warnings.
Enable HTTPS across the entire site, then redirect HTTP requests to the secure version. A partial setup can create mixed-content warnings or leave certain pages exposed. Check that your certificate renews automatically and that redirects still work after website changes, domain updates, or a migration.
SSL is essential, but it does not stop malware, brute-force login attempts, or vulnerable plugins. Treat it as a required layer, not the complete security plan.
Control Who Can Access Your Site
Many website incidents begin with legitimate credentials used in the wrong hands. Shared logins make that problem harder to trace and harder to contain. Every person who needs access should have an individual account with only the permissions required for their job.
Use long, unique passwords generated and stored in a reputable password manager. Do not reuse a hosting, WordPress, email, or domain password on any other service. If one outside account is breached, reused credentials can expose your entire web presence.
Multi-factor authentication adds a critical second check for hosting dashboards, domain registrars, content management systems, business email, and payment accounts. Even if a password is stolen, an attacker may be blocked without the second verification factor.
Review access when employees leave, contractors finish work, or an agency relationship changes. Remove accounts that are no longer needed instead of assuming they will remain inactive. For agencies and resellers, this should be part of every client offboarding process.
Keep WordPress, Plugins, and Themes Clean
WordPress is widely used because it is flexible and easy to manage, but its large ecosystem requires attention. The most common risks are outdated plugins, abandoned themes, poorly coded extensions, and plugins installed from untrusted sources.
Install only software you need, and remove inactive plugins and themes rather than leaving them dormant. An unused plugin can still contain a vulnerability. Before adding a new extension, check when it was last updated, whether it has an active support history, and whether it is truly necessary for the site.
Avoid nulled or pirated premium themes and plugins. They often contain hidden malware, backdoors, or code that sends administrator access to a third party. The initial savings rarely justify the recovery cost.
For business-critical WordPress sites, use a staging environment when possible. Test updates before applying them to the live site, especially when your site relies on eCommerce, memberships, booking tools, or custom integrations. A tested update process protects both security and uptime.
Build Backups Into Normal Operations
A backup is your recovery plan when prevention fails. It can restore a site after malware, accidental deletion, a failed update, file corruption, or an operational error. The question is not whether you need backups. It is whether they are frequent, complete, and recoverable.
A useful backup includes website files, databases, email data when applicable, and configuration details needed to restore service. Keep copies separate from the live hosting account so an attacker or server-level issue cannot affect both the site and its only backup.
Backup frequency depends on how often your information changes. A static company site may need daily backups. An online store with orders and inventory updates may need more frequent database backups. Retention matters too: if malware sits unnoticed for several weeks, you may need a clean restore point from before the infection.
Test restoration periodically. A backup that has never been restored is an assumption, not a recovery plan. Confirm who can access backups, how long a full restore takes, and what business data may need to be recreated after recovery.
Add Active Protection and Monitoring
Preventive controls reduce risk, but active monitoring helps catch suspicious activity before it becomes a larger outage. Website security tools can scan for malware, identify vulnerable software, monitor blacklisting, and alert you to unexpected changes. A web application firewall can also filter common malicious requests, including attempts to exploit known vulnerabilities.
For many small businesses, managed security services are practical because they reduce the need to interpret every alert internally. For developers with specialized requirements, server-level controls such as firewall rules, file integrity monitoring, log review, and intrusion detection may be appropriate. The trade-off is management time: advanced tools are valuable only when someone is responsible for reviewing and responding to them.
Email security belongs in this conversation as well. Phishing messages frequently target administrator credentials and domain accounts. Use spam filtering, multi-factor authentication, and clear internal procedures for handling password resets, invoice changes, and domain-related requests.
Prepare for an Incident Before One Happens
A security incident is easier to manage when decisions are already documented. Create a short response plan that identifies who can contact the hosting provider, who has domain access, where backups are stored, and who communicates with customers if an outage occurs.
If you suspect compromise, act quickly. Change passwords from a clean device, revoke unknown user accounts and API keys, preserve relevant logs, scan the site, and restore from a verified clean backup if needed. Do not simply delete a visible malicious file and assume the problem is solved. Attackers may leave hidden access points, modified database entries, or scheduled tasks behind.
A dependable hosting partner can make this process less stressful by providing responsive support, secure account tools, backup options, and services that match your site’s needs. Charter Hosting helps businesses build those layers from the domain and SSL certificate through managed hosting and website protection.
Security work is ongoing, but it does not need to be complicated. Set a maintenance routine, limit access, keep reliable backups, and choose infrastructure you can manage with confidence. Those habits protect more than a website – they protect the business that depends on it.