A promotion, product launch, or viral post can turn a normally healthy website into a slow and frustrating experience within minutes. When every visitor is directed to one server, that server becomes a single point of congestion and, potentially, failure. This guide to website load balancing explains how businesses distribute traffic across infrastructure so sites remain fast, available, and ready to grow.
Load balancing is not only for enterprise websites with millions of visitors. It can be a practical next step for an eCommerce store seeing seasonal spikes, a busy WordPress site, a growing SaaS application, or an agency managing client sites with higher uptime expectations. The right setup depends on your traffic pattern, application design, budget, and tolerance for downtime.
What Website Load Balancing Does
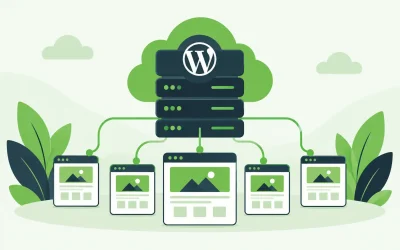
A load balancer sits between visitors and your web servers. Instead of sending every request to one machine, it directs requests to multiple available servers based on rules you set. This spreads the work, reduces the chance that one server becomes overloaded, and provides a fallback if a server stops responding.
For example, imagine an online store running on three web servers. When a customer opens a product page, the load balancer sends that request to the server with capacity to handle it. If one server fails a health check, the load balancer removes it from rotation and continues sending visitors to the remaining healthy servers.
This approach improves availability, but it does not automatically fix every performance issue. A slow database, unoptimized images, inefficient application code, or a poorly configured cache can still create delays. Load balancing works best as part of a broader hosting plan that includes monitoring, security, backups, and enough compute resources for your real workload.
How a Guide to Website Load Balancing Starts: Traffic Rules
Load balancers use algorithms to decide where each request should go. The best choice is usually based on how predictable your traffic is and whether your application needs visitors to stay connected to the same server.
Round robin is the simplest method. It sends requests to servers in sequence: first server one, then server two, then server three, and repeats. It works well when servers have similar capacity and requests are generally similar in size.
Weighted round robin is useful when servers are not identical. A newer server with more CPU and memory can receive a larger share of requests, while an older or smaller server receives fewer. This can be an effective way to expand infrastructure without replacing everything at once.
Least connections sends traffic to the server handling the fewest active connections. This can make more sense for applications where some requests stay open longer than others, such as logged-in dashboards, chat features, or application programming interfaces.
IP hash uses a visitor’s IP address to consistently send that visitor to the same server. This can help older applications that store session information locally, although it is often better to move session data into shared storage so your environment can scale more cleanly.
Health Checks Are What Make Failover Work
Distributing traffic is only half the job. A load balancer must also recognize when a server is unhealthy. Health checks perform that work by regularly testing each server through a specific port, page, or application endpoint.
A basic health check may confirm that a web server responds over HTTPS. A more useful check can verify that the application itself is working, such as a status page that confirms it can reach its database or cache. If the check fails repeatedly, the load balancer stops routing new requests to that server.
Health checks need careful configuration. If they are too sensitive, a brief network delay may take a healthy server out of service. If they are too lenient, visitors may continue reaching a server that is already failing. Set sensible intervals and failure thresholds, then test your failover process before you need it during an outage.
Layer 4 vs. Layer 7 Load Balancing
Load balancing is commonly handled at Layer 4 or Layer 7 of the network stack. The distinction affects how much the load balancer can inspect before making a routing decision.
Layer 4 load balancing routes connections based on network details such as IP addresses and ports. It is typically fast and straightforward, making it a good choice when you need to distribute TCP or UDP traffic without examining web requests.
Layer 7 load balancing understands HTTP and HTTPS traffic. It can route requests based on hostnames, URL paths, headers, cookies, or request methods. For instance, it can send traffic for shop.example.com to one application pool and api.example.com to another, or route /images/ requests to a separate service.
Layer 7 provides more control, but it also requires thoughtful configuration. If the load balancer terminates SSL connections, it must be configured with valid certificates and secure cipher settings. It must also pass the original visitor IP address through appropriate headers so your application logs, rate limits, and security tools retain useful information.
Prepare the Application Before Adding Servers
A common mistake is adding a second web server before confirming the application can run across multiple servers. If each server stores critical files, sessions, or uploads locally, visitors may see inconsistent results depending on where their request lands.
Start by making your web tier stateless where possible. Store user sessions in a shared database, cache, or session service instead of local server memory or disk. Put uploaded media in shared object storage or a shared file system. Keep application code and configuration synchronized through a deployment process rather than manual edits on individual servers.
Database capacity deserves the same attention. Multiple web servers can increase the number of requests reaching the database, which may expose a new bottleneck. Query optimization, indexing, caching, connection limits, and read replicas may all become relevant as traffic rises. Load balancing web traffic does not eliminate the need to size the database correctly.
When Your Site Is Ready for Load Balancing
You do not need to wait for an outage to consider a load-balanced environment. It is worth evaluating when traffic regularly pushes server resources high, when a short period of downtime would materially affect revenue or operations, or when your business needs maintenance windows without taking the site offline.
A single shared hosting account or entry-level virtual server can be the right fit for a new site with modest traffic. As demand becomes more consistent, a VPS or cloud environment offers greater control over server resources and configuration. Sites with sustained demand, custom applications, or stricter availability requirements may need multiple VPS instances, cloud servers, or dedicated infrastructure behind a load balancer.
At Charter Hosting, that progression can be planned without treating each stage as a completely separate technology decision. The goal is to select infrastructure that fits current demand while leaving room for measured growth.
A Practical Implementation Plan
Start with baseline data. Review traffic peaks, CPU and memory use, response times, error rates, bandwidth, and database performance. This shows whether traffic distribution is the real need or whether a smaller change, such as caching or a server upgrade, will solve the immediate problem.
Next, build a second application server that matches the first one. Use the same operating system, web server settings, runtime version, application code, and security controls. Move sessions and uploads to shared services before directing production visitors to both servers.
Then configure the load balancer, health checks, and SSL settings. Test normal traffic, a server failure, a deployment, and recovery after the failed server returns. Monitor the system closely after launch, especially during predictable high-traffic periods.
Security should remain part of the design. Restrict direct access to backend servers where possible, keep software patched, use firewalls and access controls, maintain backups, and monitor logs for unusual activity. A load balancer improves availability, but it should not become the only security control or the only point that receives attention.
The most useful next step is simple: measure your busiest hour and identify the first component that would fail if traffic doubled. That answer will tell you whether load balancing belongs in your next hosting upgrade or whether your site needs a different performance improvement first.